Update on Revolute. Not good!
1 Like
Sure. A honest mistake.
Incompetent mistake IMO. They should of used Scam Guard
If what I’ve heard (that the attackers breached the Italian regulators and use legitimate accounts) is true, scam guard would not have helped…
1 Like
This is smart. Hacking a bank? Quite hard. Hacking the windows XP computers of the government, not easy but less of a challenge 
And Scamguard is expensive for home use by a retired couple.
I was about to ask where the Italian government link came from…but, here:
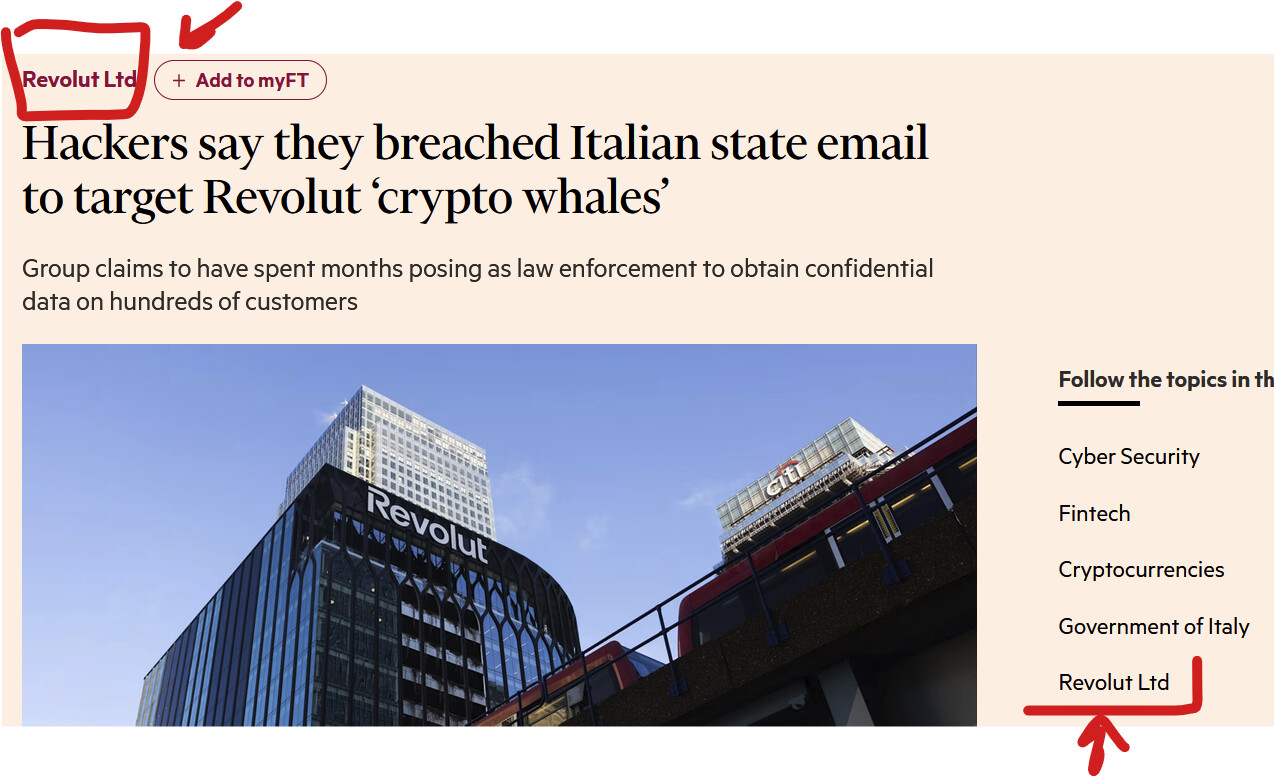
Hackers say they breached Italian state email to target Revolut ‘crypto whales’
(Hacker) Group claims to have spent months posing as law enforcement to obtain confidential data on hundreds of customers
Hackers who claim they were behind a data breach at Revolut say they obtained confidential customer information by compromising an Italian government email system and exchanging messages with the online bank over several months while posing as law enforcement.
The claims, made in a series of messages sent to the FT, suggest the hack affecting almost 700 Revolut customer accounts was more extensive than the data breach first acknowledged by the payments group on Friday. In messages sent via Telegram, a hacker or hackers using the pseudonym iamnotavillain said they had first contacted Revolut a “couple of months ago, posing as a law enforcement entity” from Italy.
Over the following weeks the hackers said they had repeatedly asked Revolut to share confidential account details for specific customers, including addresses, phone numbers and transaction histories, claiming the information was needed for ongoing law enforcement activities. “Revolut was complying like a ‘good boy’,” the purported hackers said.
The curious thing is that this can reach far beyond Revolut.
A person familiar with the matter confirmed that the requests Revolut received had come via Italy’s PEC system and the email exchanges had continued for several months. PEC is a secure network overseen by a government agency that is used by Italian authorities, companies and private citizens to send official or legal correspondence — the digital equivalent of registered post.
Revolut says limited number of impacted individuals, the hackers say:
The hacker’s requests for customer information do not appear to have been random. The group told the FT they selected the 680 targets by using blockchain analysis to identify Revolut accounts with significant crypto holdings.
Most of the 680 customers came from Switzerland and France but Revolut also handed over data on residents in 31 other mainly European countries, including the UK, Germany and Spain, the hackers added.
It may looks like shits and giggles, but there’s a history of “crypto whales” or family members being kidnapped, tortured and more to get access to crypto savings.
But…wait a min, there are 2 Revolut entities. One in the UK, servicing customers in the UK. And, one in Lithuania servicing the EU + EEA.
The FT identifies the organisation as Revolut Ltd, the UK one. Why would an UK entity answer to EU regulators? Did Brexit not happen or is the FT misidentifying Revolut Ltd?
You don’t even need to hack the PC…
Most PEC mailbox providers have webmail, as long as you can phish the owner + get MFA somehow, you are golden.
Would be trivial for an insider to support, or find a less tech savvy government employee - register a second MFA device on their account, and bob’s your uncle.
IMO, this “hack” is the digital equivalent of sending a signed for letter to revolut, asking them to provide some audit/KYC evidence, and putting a return address of the real government entity.
1 Like
I really like this kind of stories because it should humble technical people (so called engineers). It shows that regardless of technical competence and code, people matters, a lot.
1 Like
Exchange of information I suspect.
There’s a protocol to verify if customers are effectively who they say they are (KYC).
I guess they’ll a develop KYR (know your regulator) protocol from now on.
Just back from lunch. Lots of laughs, a colleague made a link to one of the most common spam phone calls:
Hello, this is the Swiss Federal Police, your Swiss identity card…and they fell for it.
The Italians have some pretty good anti-mafia / anti-money laundering laws. So much so, that even Swiss banks share information with them.
Wouldn’t be difficult for an Italian regulator to say “hey, Axa is suspected of money laundering. Prove to us that Axa is really who they say they are, and that they are not using the millions they have in their revolut wallet to fund daesh”.
What worries me more is… what next.
Because with the KYC info being leaked, yes it’s annoying - but just gathering that info is unlikely to the the ultimate goal.
So either they were blackmailing revolut… or they would use that info to do password resets and then access your wallet… or create new accounts with your info…
1 Like
They targeted Bitcoin owners. Now they have their photo and home address, I suspect that some of them will get visitor armed with pliers and blowtorches.
1 Like
Password reset is the nice way. The not-so-nice way:
I guess there’s another piece of info unmentioned for now: Revolut to base 40% of its global workforce in India by 2026. It’s unclear now which office released the data, but that willl be known sooner than later.
By a weird coincidence, in Aargau someone was strangled and threatened at knife point just last week by 2 intruders during the night.
He gave them his phone and some money… and they were promptly arrested at the train station shortly after.
Ohh, the timing:
(16.06.2026) Revolut applies for Swiss banking licence and commits CHF 150 million investment
Revolut has applied for a local banking licence from the Swiss Financial Market Supervisory Authority (FINMA). The application is currently under review.
Obtaining the licence would pave the way for a complete banking offering in Switzerland, including Swiss IBANs, salary accounts, eBill, merchant acquiring, deposit protection under Swiss standards, and the possibility of a future Pillar 3a and Twint offering.
1 Like
That seems to be coffee money that can be scratched together with some credit by any small financial company.
I think the best part of this company is it’s name, even I did not (and never would) use it.
3 Likes
That explains everything!